News
Off-boarding an employee without losing their data: a checklist for IT and MSPs
When an employee leaves, Microsoft 365 gives you 30 days and Google Workspace gives you 20 before their mailbox and files are gone for good. Here is what actually happens to a departed user's data under each platform's defaults, and a checklist for IT and MSPs that makes the deadline stop mattering.
An employee hands in their laptop on Friday. HR closes the file, IT disables the account, and the licence is reclaimed to save the next month's fee. Six weeks later, a customer asks about a quote that only ever lived in that person's mailbox, and the mailbox is gone.
This happens far more often than it should, and it rarely happens because anyone did anything wrong. Both Microsoft 365 and Google Workspace keep a departed user's data for a short while, then delete it. The default windows are measured in days, not months. Everything beyond that depends on licences, retention policies and transfer steps that have to be set up before the account is touched.
Offboarding sits in the gap between HR and IT. HR owns the timeline, IT owns the systems, and the data belongs to the business. For an MSP running tenants for dozens of customers, the same gap exists dozens of times over. This article walks through what the two platforms actually do by default, where the laptop fits in, and why a backup taken before the licence is removed is the one step that makes the rest of the checklist forgiving.
What Microsoft 365 does by default
The short version: once the account is deleted, you have 30 days. After that the mailbox is gone and the OneDrive is on its way to the recycle bin.
The details matter, because the clock starts at different points depending on what you did first.
Data | What happens by default | Window |
|---|---|---|
Mailbox, after licence removal only | Mailbox becomes disabled; email, contacts and calendar are retained, then permanently deleted | 30 days |
Mailbox, after account deletion | Mailbox is recoverable by restoring the account; after that it is purged | 30 days |
OneDrive, after licence removal only | Files stay accessible to admins as long as the account exists | No deletion while the account exists |
OneDrive, after account deletion | Retained for the OneDrive retention period, then moved to the site collection recycle bin | 30 days (configurable 30–3650), then 93 days in the recycle bin |
Teams chats, SharePoint files | Live in other mailboxes and sites, not the user's; unaffected by the user deletion | Follow their own retention |
A few things catch people out:
Licence removal is enough to start the mailbox clock. You do not need to delete the account. Reclaiming the licence on departure day and deleting the account a quarter later is the normal sequence, and it quietly costs you the mailbox after 30 days.
The 30-day OneDrive setting is a tenant-wide default. It can be raised to ten years in the SharePoint admin center, but only for users deleted after the change. It does nothing for users already deleted.
"Inactive mailboxes" are not free. Microsoft can keep a departed user's mailbox indefinitely without a licence, but only if a retention policy or litigation hold was applied before the account was deleted. That requires a Microsoft 365 E3/E5 or equivalent compliance licence and someone who set it up in advance.
Converting to a shared mailbox is a half-measure. It keeps the email searchable without a licence, but shared mailboxes have a 50 GB cap, keep no OneDrive, and are still a single live copy inside the tenant. Ransomware, an admin mistake or a tenant breach takes the shared mailbox along with everything else.
The admin centre offers to hand access to another user. That is a convenience for the manager, not a preservation step. The 30-day window applies just the same.
Sources: Microsoft's documentation on deleting a user, OneDrive retention and deletion, setting OneDrive retention for deleted users and removing a former employee.
What Google Workspace does by default
Google's window is shorter: 20 days from deletion, and the Drive files only come back if you restore the whole account.
Google has no equivalent of Microsoft's "remove the licence and keep the account" halfway state, because a Workspace user always consumes a licence. The practical choices are suspend, delete, or move the user to a paid Archived User licence.
Data | What happens by default | Window |
|---|---|---|
Gmail | Retained with the deleted account; recoverable only by restoring the user | 20 days |
Drive files the user owns | Saved, but not accessible to anyone unless the user is restored; after that, deleted | 20 days |
Drive files others own, in the user's folders | Still findable by people who already had access; then moved back to the owners' My Drive | 20 days |
Primary calendar | Retained with the deleted account | 20 days |
Shared drives | Owned by the team, unaffected by the user deletion | No change |
The corners worth knowing:
Transfer is a manual step at deletion time, and only a super admin can do it. The delete dialog offers to hand Drive, Docs, Calendar and Looker Studio data to another user. If a delegated admin deletes the user, or someone clicks "Don't transfer data", that offer is gone.
Gmail is not in that dialog. Moving a departed user's mail to another account means the data migration service, a Vault export, or a Takeout run before the account is touched. None of that happens by itself.
A failed transfer is easy to miss. Google suspends the user while the transfer runs; permission errors and large Drives can leave files behind, and the 20-day clock does not pause.
Restoring the user needs a free licence. On an annual or fixed-term plan that may mean buying one. On day 21 it does not matter; the account and its data are gone.
Archived User licences are Google's long-term answer, and they are a decent one: cheaper than a full seat, data retained under Vault rules. They still require a Vault-capable edition, a per-user fee for as long as you keep the data, and the data remains a single copy inside the tenant.
Sources: Google's documentation on deleting or removing a user and restoring a deleted user's Drive files.
The laptop
The cloud tenant is only part of the picture. The laptop that comes back on departure day usually holds data that never reached OneDrive or Drive at all.
Where it hides:
Local folders outside the sync root. Downloads, the Desktop (if Known Folder Move was never enabled), a
C:\workdirectory someone created in 2021, the home folder on a Mac.Sync that silently stopped. A sync client signed out months ago, a quota that filled up, a file type the client refuses to upload. The user saw a green tick last year and assumed it was still true.
Application data. Outlook PST archives, local Git clones with unpushed branches, database exports, CAD and design files too large for the sync client, browser profiles with saved work.
Mobile devices. Photos and voice notes from site visits that only exist on a phone that is about to be wiped.
And two ways to lose what is there:
Disk encryption. BitLocker and FileVault are the right default, but if the recovery key was only ever in the user's personal Microsoft or Apple account, the data is locked when the account is disabled. Keys should escrow to Entra ID, Intune, or your MDM before a device is ever handed over.
Remote wipe on departure. Intune, Jamf and Workspace device management all let you wipe a device the moment an account is disabled. That is correct for a lost device. On an off-boarding day it runs before anyone has looked at the disk.
The fix is the same as for the tenant: take a full backup of the laptop before the account is disabled and the device is wiped or re-imaged. A file-level backup of the user profile is usually enough; it is small, it is fast, and it is the difference between "we have it" and "we think it synced".
Why a backup before license removal is the only reliable answer
Every option the platforms offer has the same shape: it works if someone set it up in advance, it is scoped to one service, and it leaves the data as a single copy inside the tenant. A backup taken while the account is still licensed has none of those limits.
Option | Needs setup before departure | Covers mail | Covers files | Covers the laptop | Survives tenant loss | Ongoing cost |
|---|---|---|---|---|---|---|
Default retention | No | 20–30 days | 20–30 days | No | No | None |
Shared mailbox (MS365) | No | Yes, 50 GB cap | No | No | No | None |
Retention hold / inactive mailbox (MS365) | Yes, compliance licence | Yes | OneDrive via policy | No | No | Licence tier |
Archived User licence (Google) | Yes, Vault-capable edition | Yes | Yes | No | No | Per user, indefinitely |
Transfer to a colleague | At deletion time, super admin | Google: no; MS365: 30-day access | Yes | No | No | None, but data is now mixed into someone else's account |
Backup before licence removal | Only the backup job | Yes | Yes | Yes | Yes | Storage only |
Three reasons this is not just one more row in the table:
It removes the deadline. Once the backup exists, the 20- or 30-day window stops mattering. HR can take their time with the exit paperwork, IT can reclaim the licence on day one, and nobody has to remember to restore an account on day 19.
It is independent of the tenant. Retention policies, holds and archived users all live inside the same Microsoft or Google account that an attacker, an over-eager admin or a billing dispute can take away. A backup in storage you control is the only copy that does not share that fate. Departed employees' data is exactly the data most likely to be needed in a dispute, an audit or a legal hold years later, so it deserves the same 3-2-1 treatment as anything else.
It covers all of it at once. Mailbox, OneDrive or Drive, calendar, contacts, and the laptop profile go into one backup set, with one retention rule and one place to search. Nobody has to piece together a shared mailbox, a transferred Drive folder and a disk image from the IT cupboard eighteen months later.
The order is the whole point. The backup has to run while the licence is assigned and the account is enabled, because that is the only time the APIs will hand the data over in full. Remove the license first and you are back on the platform's clock.
The checklist
The sequence matters more than the individual items: back up, then hand over, then revoke, then reclaim. Most off-boarding failures come from running the last two steps first.
Before the last day (HR notifies IT)
HR sends IT the departure date and the user's manager as soon as notice is given, not on the last day
Confirm the user is covered by the MS365 or Workspace backup and that the latest run succeeded
Confirm the laptop is in the endpoint backup and the last run is recent; if not, run one now
Verify the disk encryption recovery key is escrowed in Entra ID, Intune, Jamf or your MDM
Ask the manager which mailbox, calendar and folders need to stay reachable, and by whom
List external services where the user is the account owner (domain registrar, payment processor, SaaS admin roles) and reassign ownership while the user can still approve it
Check for personal-account dependencies: 2FA tied to a personal phone, recovery emails, files shared from a personal Drive
On the last day
Run a final, complete backup of mailbox, OneDrive/Drive, calendar and contacts while the license is still assigned
Run a final backup of the laptop before it is wiped, reimaged or reassigned
Set up an auto-reply and mail forwarding to the manager or a shared inbox
Google: suspend the user rather than delete; transfer Drive and Calendar ownership to the manager
Microsoft: convert the mailbox to shared if colleagues need live access; delegate OneDrive to the manager
Revoke sessions and tokens, reset the password, remove MFA devices, remove from groups and SSO apps
Wipe or re-image the laptop only after the backup is verified
After the last day
Reclaim the license (Microsoft) or delete the suspended user (Google) once the backup and handover are confirmed
Record where the backup lives, its retention period, and who can restore it, in the HR exit record
Set a retention rule for departed-user backups that matches your legal and contractual obligations, typically years rather than months
Test a restore of one mailbox item and one file within the first week, before anyone needs it for real
For MSPs: do all of the above per tenant, and keep the departed-user backups in the customer's own retention tier so the data stays with the customer if they leave you
For an MSP the list is the same, but the trigger is different: the customer tells you, often late, and often by ticket. The step that saves you is the one that does not depend on being told in time. If every user in every tenant is already in a scheduled backup, the last-day items become confirmation, not rescue.
How this works with Duplicati
The managed Microsoft 365 and Google Workspace backups in the Duplicati Console are built for exactly this sequence. Every licensed user in the tenant is backed up on a schedule, so the "final backup" on departure day is already there before anyone asks for it.
What that looks like in practice:
Per-user seats, not per-tenant guesswork. Each MS365 or Workspace seat covers one user's mailbox, files, calendar and contacts, and brings 100 GB of storage with it for managed backups. When a user leaves, the seat can be freed while their backup stays in retention.
Storage you control. Backups go to Duplicati-provided storage by default, encrypted with a key you hold, or to any destination you already use. Either way it sits outside the Microsoft or Google tenant, so a tenant problem does not become a backup problem.
Restore to the same tenant or a different one. A departed user's mailbox can be restored into their old account, into the manager's, or into another tenant entirely. That last case matters for MSPs handling a customer migration or an acquisition.
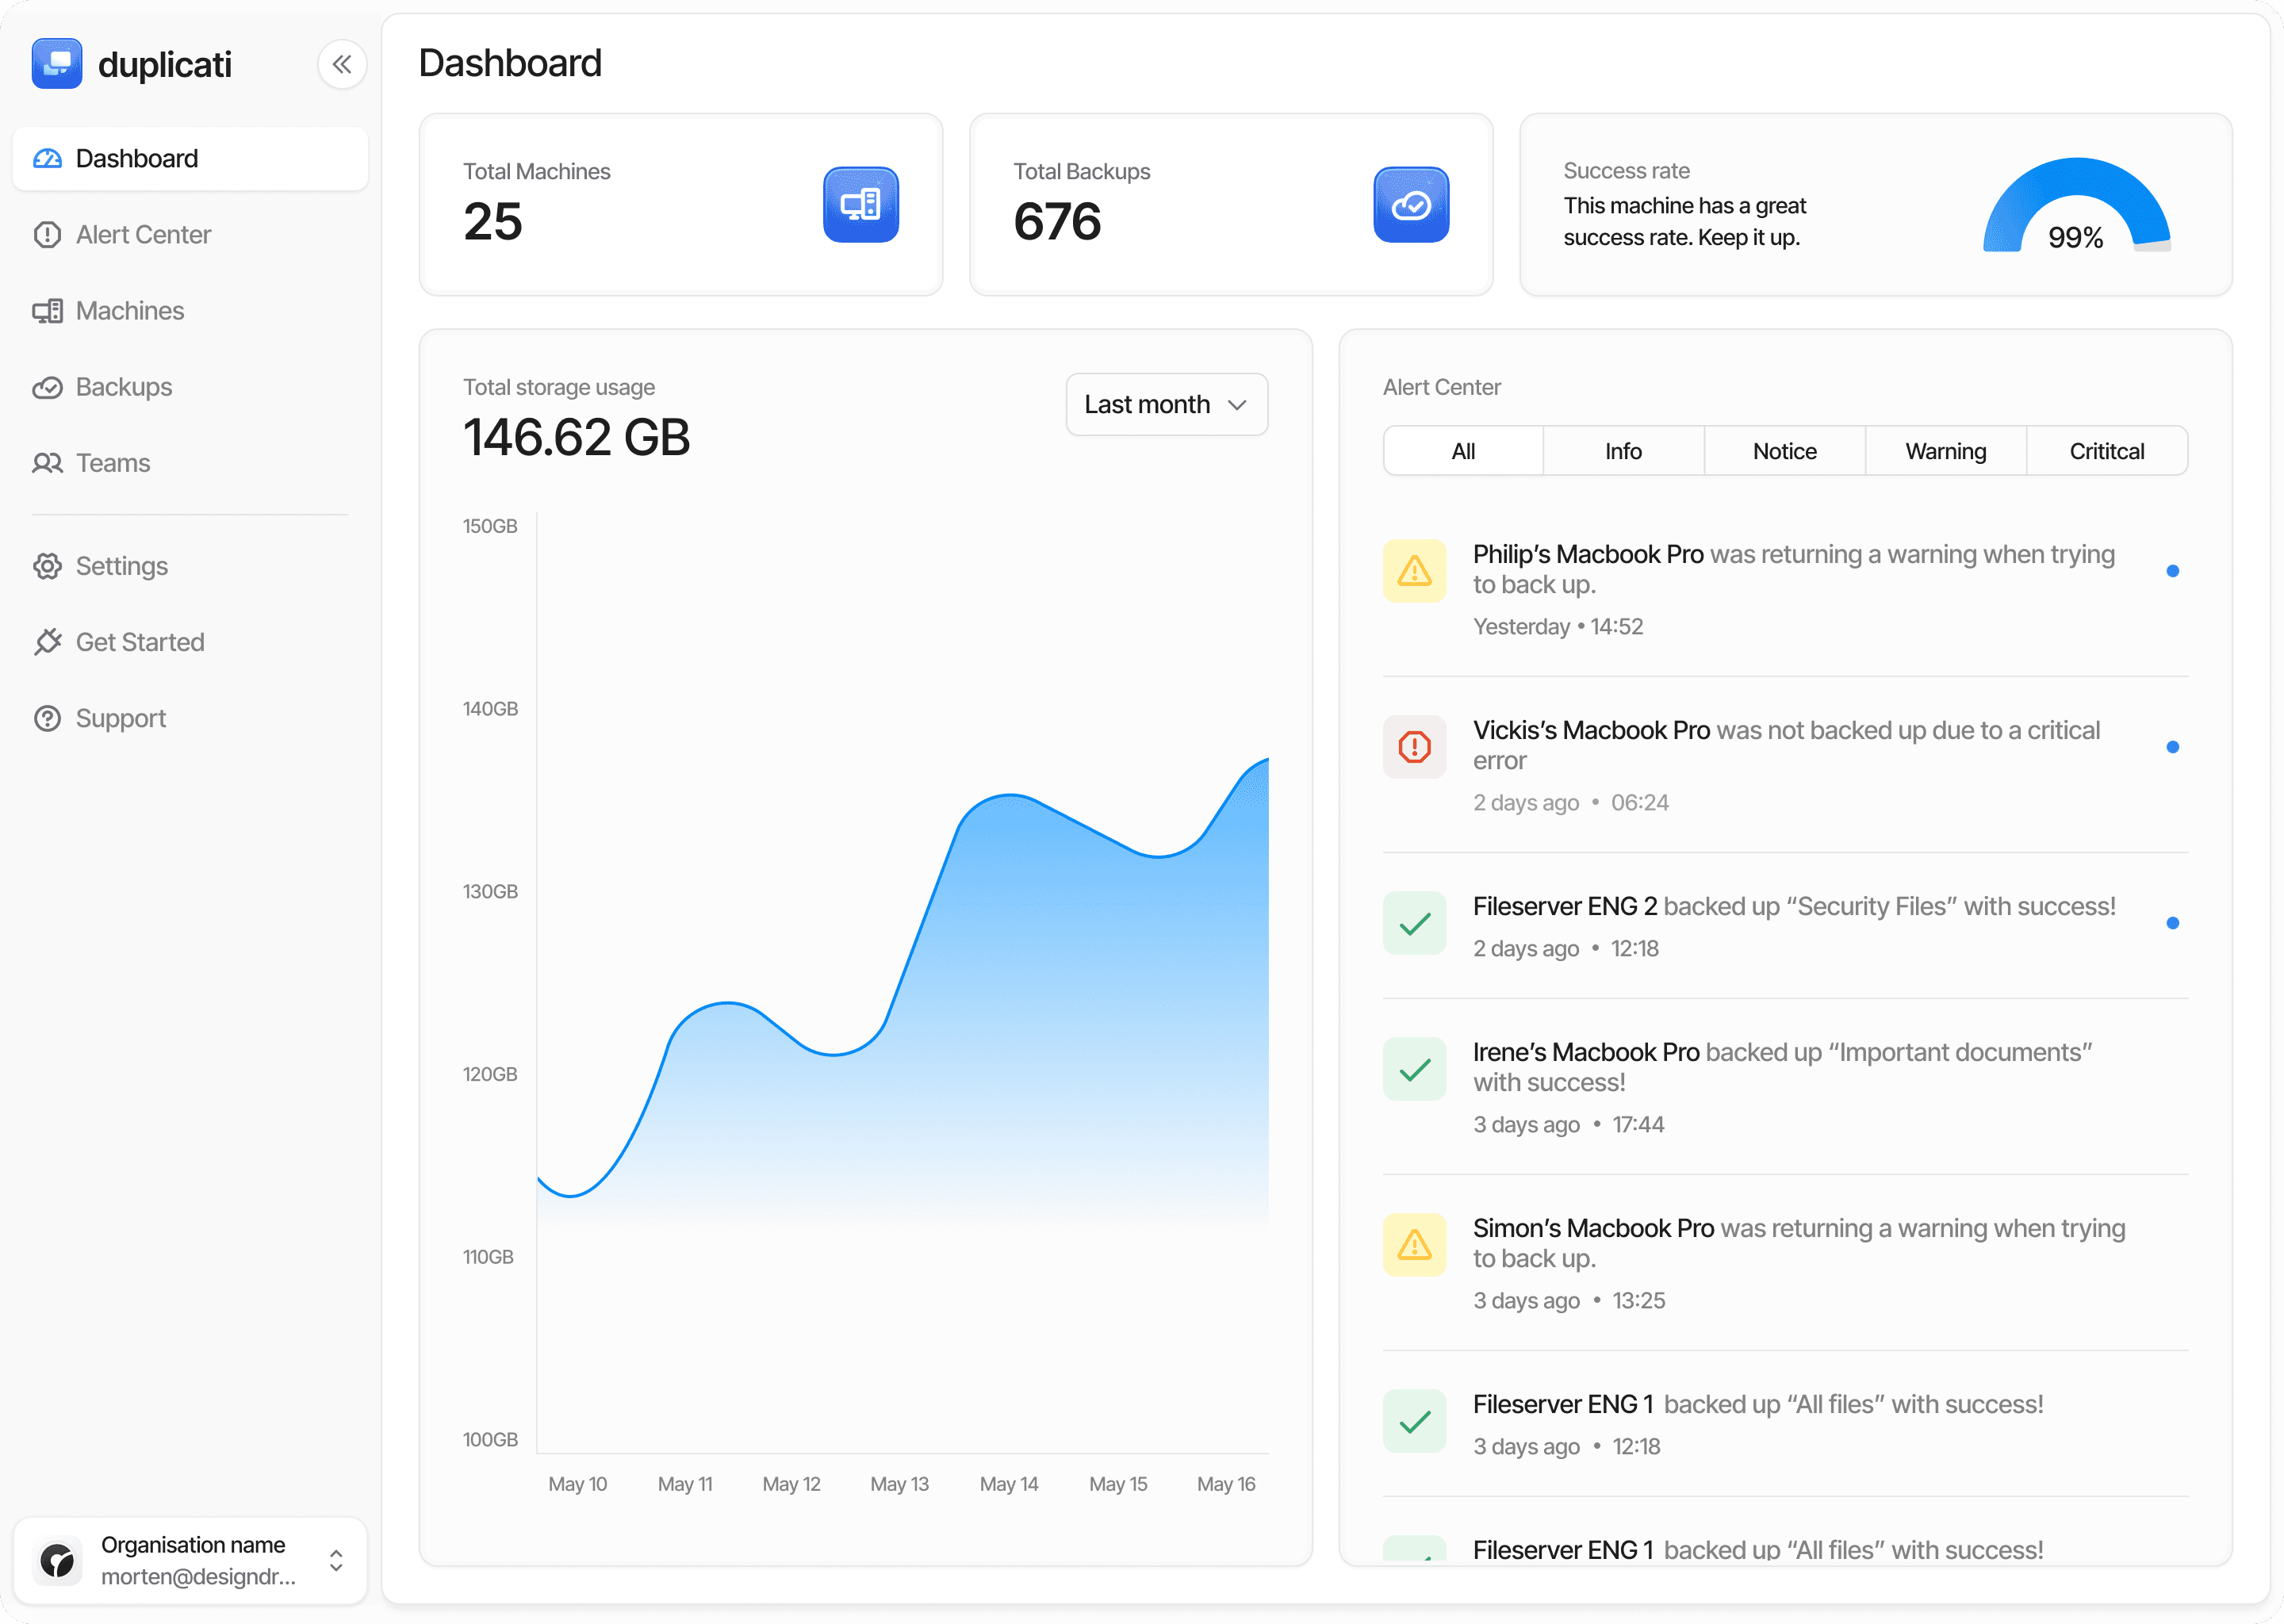
Laptops in the same console. The Duplicati agent on the endpoint backs up the user profile to the same storage and shows up in the same dashboard, so one place answers "do we have everything from that person?"
One view across all tenants. For an MSP, the Console shows every customer's users and every backup's last successful run, which is where the "before the last day" checks above actually get done.
Off-boarding will always be a handover between HR and IT, and the handover will sometimes be late. The way to make it forgiving is to stop depending on the timing: back up every user continuously, keep departed users' data on your own retention terms, and let the license go the moment HR says so.
If you manage Microsoft 365 or Google Workspace tenants and want the final backup to already exist on departure day, managed MS365 and Workspace backup in the Duplicati Console is the place to start.